Endpoint security
Bastion
Endpoint security for orgs enterprise left behind.
Endpoint security across a Rust agent, ingestion backend, and native console.
- My role
- Co-Founder & CTO · Product design & engineering
- Period
- 2025–ongoing
- Built with
- Rust · Axum · Tonic / gRPC · SurrealDB · Flutter · YARA-X
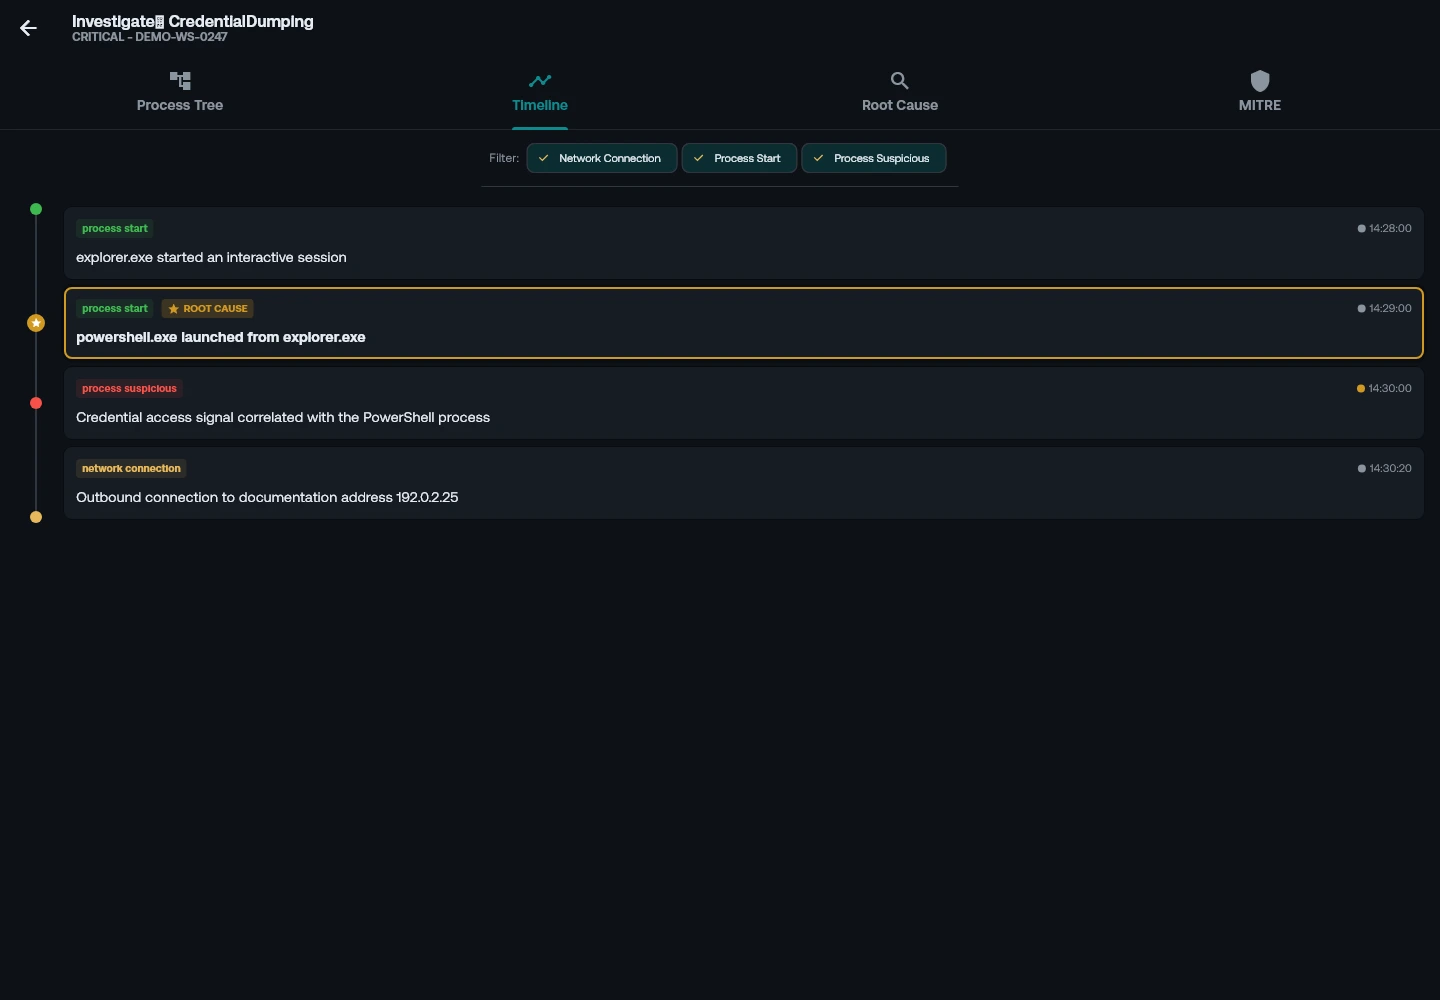
Concurrency made detection slower, so it stayed sequential
2×
Each security event passes through seven detection layers, and running them concurrently looked like an easy win. I split the layers into independent units, built a concurrent Tokio dispatch, and benchmarked it on the real hot path. It was twice as slow: most layers cost under a microsecond, and dispatching tasks cost more than the work they overlapped.
I kept the sequential path, added a test that both paths reach the same result, and documented when to switch: a heavier model or a large YARA scan.
Two writers forked the audit trail
Bastion keeps a hash-chained audit log so tampering is detectable. Its two writers each kept their own chain head, so concurrent writes forked the chain and verification flagged real entries as failures. One shared head now links every entry, and a test interleaves 100 writes from both writers and verifies the chain.
A compliance score of 100 when nothing could be read
HIPAA and FERPA dashboards scored 100/100 when their database reads failed, and saved that score. Read failures now surface as errors, and the compliance endpoint returns one when a score input cannot be read.
Have a project in mind?
I’m open to product engineering roles and contract work.